User Self-Service
Give employees a paperless portal to manage profiles, submit GxP access requests, request password resets with admin approval, and receive status notifications — with approval routing through department heads and QA.
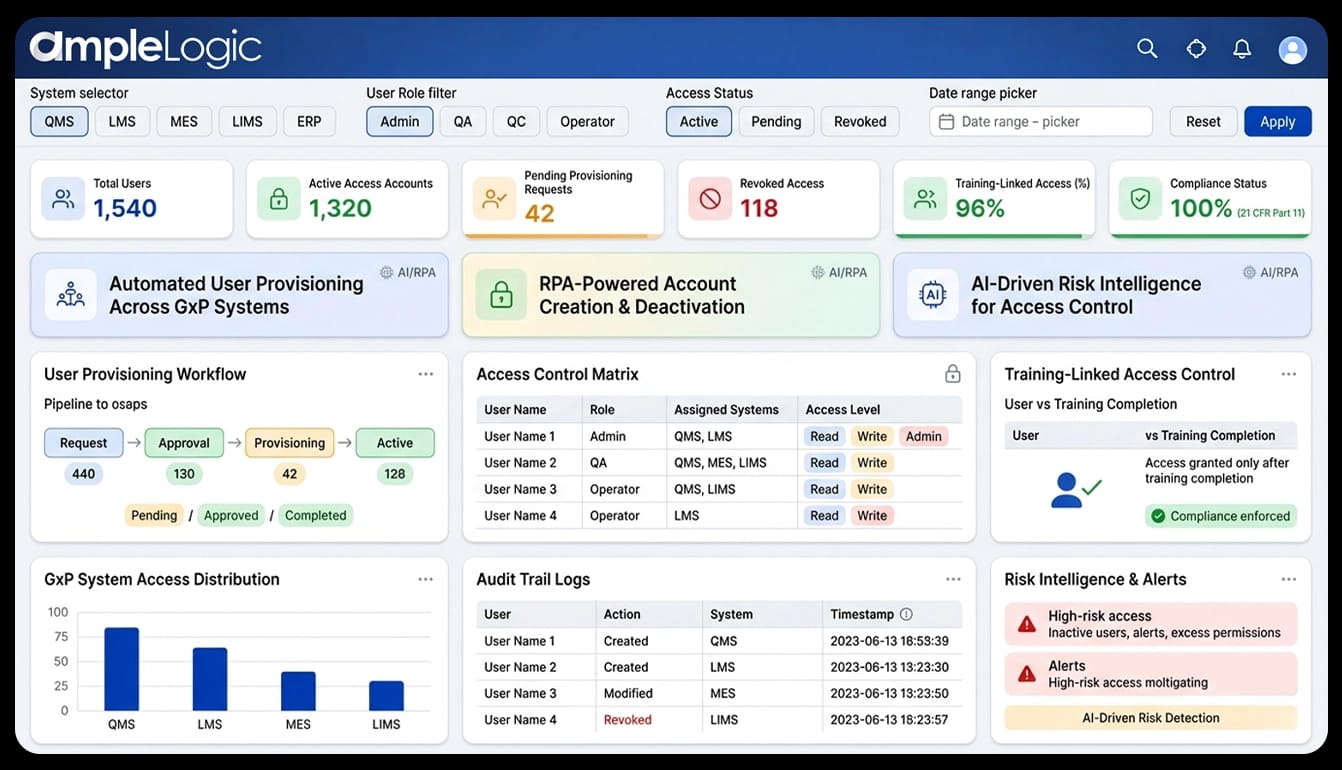
Replace paper and email access requests with a governed portal
Lab analysts, scientists, and operators often need new roles, profile updates, or password help while IT and QA are already overloaded. Email and paper forms lack clear routing, status visibility, and electronic signature evidence.
User Self-Service in AmpleLogic User Access Management focuses on what the parent product delivers for end users: electronic access requests, employee profile management, password reset flows with admin approval, and notifications on request progress — plus role-change requests with multi-level approval where configured.
Self-service reduces friction; approvals, SoD checks, and admin controls remain part of the path before sensitive GxP access is granted.
Explore AmpleLogic User Access ManagementWhat User Self-Service enables
Practical capabilities IT, QA, and operations teams use to govern GxP identities and access.
Electronic Access Requests
Web-based, paperless access request portal with a GxP role catalog, approval routing through department heads and QA, SLA tracking, and Part 11-oriented electronic signatures.
Employee Profile Management
Self-service profile updates synced with HR systems, including qualifications, training history, site assignments, and department transfers used in access governance.
Password Reset with Admin Approval
Request password resets through the portal with verification and admin approval so scientists regain access without unmanaged workarounds.
Request Status Notifications
Notify requesters as access and reset requests move through submission, approval, and completion so status is visible without chasing email threads.
Role Change Requests
Scientists and operators can request role changes with justification, multi-level line-manager and QA approval, and SoD conflict detection before granting.
How this capability fits the user access management lifecycle
From account provisioning and policy through reporting, alerts, and self-service requests.
Step 01
Open the portal
Employees sign in to view assigned roles, profile details, and available request options.
Step 02
Submit a request
Choose access, role change, profile update, or password reset from the governed catalog.
Step 03
Route for approval
Send requests through department heads, QA, and administrators based on configured workflows.
Step 04
Notify progress
Keep requesters informed as approvals complete or additional information is needed.
Step 05
Fulfill & activate
Apply approved access or password changes under admin controls and training rules where required.
Step 06
Retain request history
Keep attributable request and approval records for later review and inspection support.
Outcomes access and quality teams can expect
Benefits focused on this User Access Management capability.
Fewer stalled email requests
Give users a single portal with SLA tracking instead of lost paper forms and inbox threads.
Clearer approval ownership
Route GxP access and role changes through department heads and QA with visible status.
Faster password recovery path
Let employees initiate resets while retaining admin approval and verification controls.
Better profile accuracy
Keep site, department, and qualification details current for access governance decisions.
Built to support regulated life sciences access governance
Controls and practices most relevant to this capability. Access controls support compliance work — they do not alone equal regulatory compliance.
Controlled request evidence
Retain electronic request, approval, and signature records that support Part 11-oriented review practices.
Approval before sensitive grants
Keep admin and QA approval in the path for access changes and password resets — self-service does not mean unsupervised privilege.
SoD-aware role changes
Detect segregation-of-duties conflicts before granting requested role combinations where configured.
Self-service connected to the rest of UAM
Portal requests depend on the role catalog, security policies, and reporting that surround day-to-day identity work.
With GxP account management
Approved requests become provisioned roles and accounts under training-linked rules.
With license & security
Granted access consumes licenses and inherits centralized security policies.
With reporting & alerts
Pending approvals and request outcomes appear in site dashboards and escalations.
Govern Access. Reduce Orphaned Accounts. Stay Inspection-Ready.
Explore User Access Management to discuss GxP provisioning, license control, and self-service requirements, or request a demo with our team.
Speak with our team about GxP account management, license tracking, alerts, and self-service access requests.
Nuestras Oficinas Globales
Estamos donde nos necesita. Conectamos a nivel global y entregamos a nivel local.
India

Melange Tower, 2nd Floor, Wing-C, Patrika Nagar, HITEC City, Madhapur, Hyderabad - 500081, Telangana, India
Estados Unidos (Dallas)

17330 Preston Road Suite 200D, Dallas, TX, 75252
Canadá (North York, Toronto)

5255 Yonge Street Suite 201, North York, ON, M2N 6P4
Australia (Melbourne)

Level 14, 330 Collins Street, Melbourne, VIC, 3000
Corea del Sur (Daegu)

Daegu Trade Centre, 8/F. 489, Dongdaegu-ro, Daegu, 41256
Irlanda (Dublín)

Block 1, Blanchardstown Corporate Park Ballycoolen Road, Dublin, D15 AKK1
Singapur

1 Scotts Road, #24-10 Shaw Centre, Singapore, Singapore, 228208
Manténgase a la vanguardia en las ciencias biológicas
Reciba las últimas actualizaciones de productos, noticias sobre cumplimiento y conocimientos de la industria en su bandeja de entrada.